Guide
What a blue hat hacker is, and what the label means for buyers
A blue hat hacker usually means an outside security professional invited to test a product before release. However, the label is also used as slang, so the context matters.
- Signed written scope first
- Senior ethical hackers only
- Your NDA signed as standard
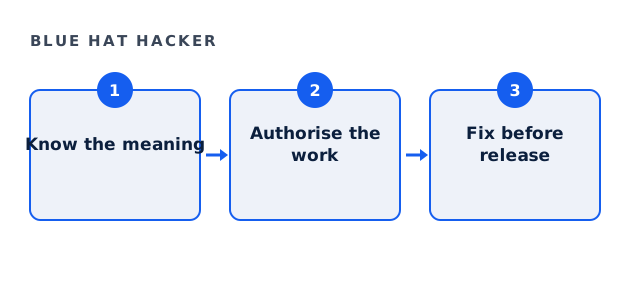
The main meaning of blue hat hacker
The term grew from Microsoft's practice of inviting outside researchers to test software before launch. Therefore a blue hat hacker is someone brought in from outside, with permission, to find flaws early.
Microsoft also runs a security conference under the BlueHat name. Also, the idea spread to other companies that invite outside testers before release.
The slang meaning
Online, some people use the phrase for someone seeking revenge through hacking. However, that use describes unlawful behaviour, and it has nothing to do with authorised testing.
Ready to bring in a blue hat hacker?
Tick what is already true.
Your result appears here as you tick, so you can see what is still open.
Blue hat hacker compared with other labels
The colours describe permission and purpose. So buyers should focus on authorisation rather than labels.
| Label | Permission | Typical role |
|---|---|---|
| White hat | Written authorisation | Ongoing authorised testing |
| Blue hat | Invited, with permission | Pre-release testing |
| Grey hat | None | Unrequested probing |
| Black hat | None | Criminal intrusion |
Engaging a blue hat hacker before release
Bring the tester in before launch, not after. For example, test a new customer portal while there is still time to fix it. Also sign a written scope, because pre-release systems still need clear boundaries.
- Agree the release timeline first
- Provide test accounts and environments
- Sign an NDA before technical detail
- Plan a retest before go-live
Working with Truevector
Our senior ethical hackers can test before release, under a signed scope and your NDA. Full engagements usually land between $35,000 and $120,000, with a floor of $25,000. The bounded External Exposure Review starts at $4,500, and its fee is credited in full against a full engagement commissioned within ninety days. More on the original practice is at Microsoft BlueHat.
Also budget time after the test. So fixes land before launch.
Blue hat hacker questions
Is a blue hat hacker legal?
Yes, when invited by the owner and working under written authorisation.
Is a blue hat hacker the same as a white hat?
Close. The blue hat label stresses outside testing before release.
Does the slang blue hat hacker meaning matter?
Only to avoid confusion. Revenge hacking is unlawful.
When should pre-release testing happen?
Early enough to fix findings before launch.
Related guides
Engage a blue hat hacker before you launch
Tell us what you are releasing and when. We reply with a written scope and a fixed fee.
Request a written scope