Guide
What a white hat hacker is, and how to engage one safely
A white hat hacker uses attacker skills with the owner's permission, so weaknesses are found and fixed before a criminal finds them. Authorisation, not technique, is what makes the work lawful.
- Signed written scope first
- Senior ethical hackers only
- Your NDA signed as standard
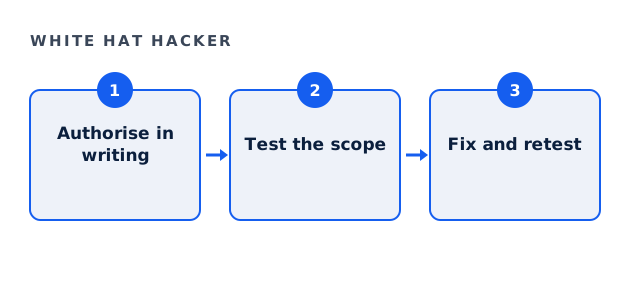
What makes someone a white hat hacker
The tools are often the same ones criminals use. However, the white hat works only on systems the owner has authorised in writing, inside an agreed scope. So the difference is permission and purpose, not skill.
That is also why the paperwork matters. A signed scope protects the client, and it protects the tester too.
White hat, grey hat and black hat
The labels describe intent and permission. Therefore they matter to anyone hiring.
| Label | Permission | Lawful? |
|---|---|---|
| White hat | Written authorisation from the owner. | Yes, inside the scope. |
| Grey hat | None, even if intentions are good. | Usually not. |
| Black hat | None, with harmful intent. | No. |
Ready to engage a white hat hacker?
Tick what is already true. Open items become part of the written scope.
Your result appears here as you tick, so you can see what is still open.
What a white hat hacker tests for a business
Most engagements look at the systems an attacker would target first. For example, web applications, APIs, cloud configuration and the internet edge.
- Web applications and the APIs behind them
- Internal and external networks
- Cloud configuration and identity
- Objective-driven red team simulations
How to engage a white hat hacker safely
Start with a written scope that lists systems in and out of bounds. Also sign an NDA before any technical discussion, and ask who exactly will test. Then confirm the method, such as the Penetration Testing Execution Standard, so the work is structured rather than improvised.
Working with Truevector
Our senior ethical hackers sign your NDA first, agree the scope in writing and brief you personally afterwards. Full engagements usually land between $35,000 and $120,000, with a floor of $25,000. The bounded External Exposure Review starts at $4,500, and its fee is credited in full against a full engagement commissioned within ninety days.
White hat hacker questions
Is hiring a white hat hacker legal?
Yes, when the system owner authorises the work in writing and the tester stays inside the scope.
Can a white hat test someone else's system for us?
No. Only the owner, or someone the owner authorises, can permit testing.
What does a white hat hacker deliver?
A written report with findings, impact and fixes, then a retest once you fix them.
Do white hats use the same tools as criminals?
Often, yes. However, permission and scope make the work lawful.
Related guides
Engage a white hat hacker with a written scope
Tell us what you need tested and why. We reply with a written scope and a fixed fee, and nothing starts before you sign.
Request a written scope