Service
OSINT penetration testing: what attackers learn about you first
OSINT penetration testing maps the information about your organisation that anyone can find publicly. So you see your footprint the way an attacker would, before they use it.
- Signed written scope first
- Senior ethical hackers only
- Your NDA signed as standard
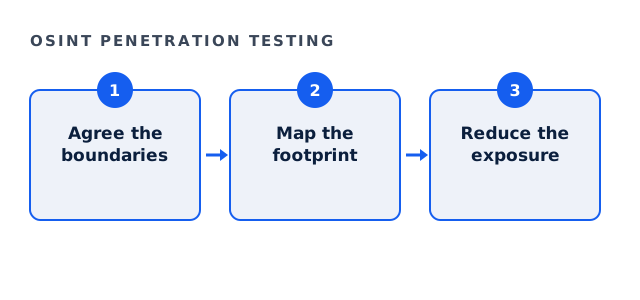
What OSINT penetration testing means
OSINT stands for open-source intelligence, meaning publicly available information. Attackers start there. Therefore reviewing it first shows where an attack would likely begin.
The work stays passive and lawful. Also, it focuses on the organisation, not on anyone's private life.
What OSINT penetration testing reviews
The review looks at the business footprint. For example, forgotten domains or code published by mistake.
- Domains, subdomains and exposed services
- Public code repositories
- Documents and metadata published online
- Staff roles that attract targeted phishing
- Mentions of your organisation in public breach reports
OSINT penetration testing readiness check
Tick what is already true.
Your result appears here as you tick, so you can see what is still open.
Boundaries in OSINT penetration testing
Clear limits keep the work ethical. So the written scope states what is in and out.
| Boundary | Rule |
|---|---|
| Targets | Your organisation only |
| Methods | Public sources, no intrusion |
| People | Business roles, never private lives |
| Data | Summarised, not stockpiled |
What you receive
You receive a written picture of your exposure and a prioritised list of fixes. Also, a senior ethical hacker walks you through it. The Penetration Testing Execution Standard describes intelligence gathering as the first phase of testing.
Often this is the right first step. In addition, it shapes the scope of any later test.
Fees
Full engagements usually land between $35,000 and $120,000, with a floor of $25,000. The bounded External Exposure Review starts at $4,500, and its fee is credited in full against a full engagement commissioned within ninety days.
Also repeat the review periodically. Because footprints grow with every new tool and hire, last year's picture goes stale. So a yearly refresh keeps exposure in view. In addition, share the findings with communications and HR teams, because much of the footprint is created outside IT. As a result, fixes happen where the exposure starts.
OSINT penetration testing questions
Is OSINT penetration testing legal?
Yes, when it uses public sources and stays within an agreed scope.
Does OSINT penetration testing touch our systems?
No. It reviews public information only.
Who is OSINT penetration testing for?
Organisations that want to see their exposure before a full engagement.
Do you look into staff private lives?
No. Only business roles and the organisation's footprint.
Related guides
Start with OSINT penetration testing
Tell us your organisation and main domains. We reply with a written scope and a fixed fee. Also say whether a full engagement may follow, because the scope can then be shaped for it.
Request a written scope