Service
Phishing penetration testing for your own organisation
Phishing penetration testing simulates the emails attackers send, aimed only at your own staff and authorised by your leadership. So you learn how your people and your email defences respond before a real attacker tests them.
- Signed written scope first
- Senior ethical hackers only
- Your NDA signed as standard
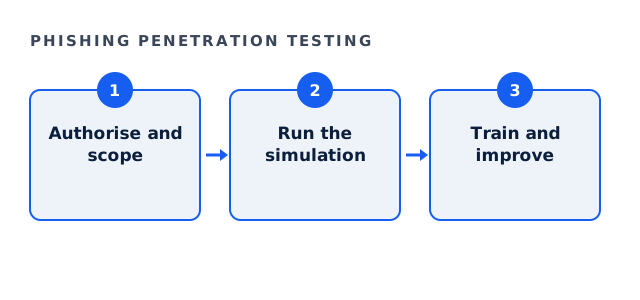
What phishing penetration testing measures
The goal is to measure defences, not to embarrass people. Therefore results focus on systems and processes.
- How many messages reach inboxes past filtering
- How many recipients report the message
- How quickly the security team responds
- Whether credentials entered would have been usable
Authorisation and fairness
Leadership authorises the test in writing, and HR agrees how results are used. So individuals are not named or disciplined from a single simulation. Also, we never target people outside your organisation.
Phishing penetration testing readiness
Tick what is agreed.
Your result appears here as you tick, so you can see what is still open.
Phishing penetration testing compared with awareness training
Training teaches, while testing measures. However, the two work best together.
| Awareness training | Phishing test | |
|---|---|---|
| Purpose | Teach what to look for. | Measure real behaviour. |
| Output | Completion records. | Report rates and response times. |
| Frequency | Ongoing. | Periodic, agreed in scope. |
How results improve defences
The most useful number is often the report rate, because early reports let the security team act fast. Also, results show where filtering or multi-factor would have stopped an attack anyway. See CISA phishing guidance for wider guidance.
Fees and fit
Phishing simulation usually sits inside a red team or adversary simulation engagement. Full engagements usually land between $35,000 and $120,000, with a floor of $25,000. The bounded External Exposure Review starts at $4,500, and its fee is credited in full against a full engagement commissioned within ninety days.
Also agree in advance what happens if a real attack arrives during the test. The security team must be able to tell simulated messages from genuine ones quickly, so a simple identifier or a briefed contact prevents confusion. Afterwards, share the overall results with staff, because transparency builds trust in the programme and encourages reporting.
Phishing penetration testing questions
Is phishing penetration testing legal?
Yes, for your own organisation with leadership authorisation and agreed rules.
Will staff be named?
Not from a single simulation. Results focus on defences and processes.
Can you phish another company for us?
No. We only test organisations that authorise us.
Does phishing penetration testing include training?
It can be paired with training, but the test itself measures behaviour.
Related guides
Scope phishing penetration testing
Tell us your organisation's size and goals. We reply with a written scope and a fixed fee. Leadership approval comes first, in writing. HR agrees the rules for results at the same time, before any message is sent.
Request a written scope