Service
Salesforce penetration testing for the data your org exposes
Salesforce penetration testing checks whether your org's configuration and custom code expose records to the wrong people. The platform is secure by design, but sharing rules, guest access and integrations are yours to get right.
- Signed written scope first
- Senior ethical hackers only
- Your NDA signed as standard
What Salesforce penetration testing covers
We test what you configured and built, so the work follows the Salesforce security assessment policy and stays inside your own org.
- Profiles, permission sets and sharing rules
- Guest user access on public sites
- Experience Cloud portals for customers or partners
- Custom Apex code and Lightning components
- Connected apps and integrations
Guest access deserves special attention
Public sites built on Salesforce can expose records to anyone if guest permissions are too broad. So we test what an unauthenticated visitor can read, because many real exposures have occurred there. Also, we check whether guest users can reach records through custom code.
Salesforce penetration testing readiness
Tick what you can provide.
Your result appears here as you tick, so you can see what is still open.
Common Salesforce penetration testing findings
Several issues appear again and again, but each is fixable.
| Finding | Impact |
|---|---|
| Over-broad guest permissions | Public visitors can read records. |
| Sharing rules wider than intended | Users see other accounts' data. |
| Custom code without access checks | Users bypass sharing rules. |
| Integrations with admin rights | One stolen token exposes the org. |
How Salesforce penetration testing runs
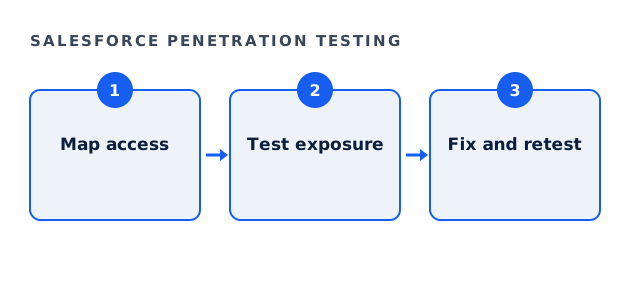
We work in a sandbox where possible, so production stays untouched, with test users for each profile. Then we try to reach records each user should not see, because that is the core risk. Finally, the ethical hacker who ran the test briefs you and retests after fixes.
Salesforce penetration testing fees
Salesforce work is scoped like a web application engagement. Full engagements usually land between $35,000 and $120,000, with a floor of $25,000. The bounded External Exposure Review starts at $4,500, and its fee is credited in full against a full engagement commissioned within ninety days. The method follows the OWASP Web Security Testing Guide.
Also review integrations whenever a new tool connects to Salesforce. Each connected app holds a token, so a forgotten integration can quietly keep wide access long after anyone uses it.
Salesforce penetration testing questions
Does Salesforce allow customers to test their org?
Yes, within its published security assessment policy, which we follow.
Can testing run in a sandbox?
Yes, and it is preferred, with read-only checks in production where needed.
Does Salesforce penetration testing include custom code?
Yes, because custom code can bypass sharing rules.
Do you test Salesforce's own platform?
No. We test your configuration and code only.
Related guides
Scope Salesforce penetration testing
Tell us your org's size, sites and integrations. We reply with a written scope and a fixed fee.
Request a written scope